HIPAA-Ready Cloud with Zero-Trust Access
A HIPAA-aligned, zero-trust cloud foundation with private GKE, automated vulnerability gates, encrypted access, and audit evidence available in minutes.
Security engineered around patient data
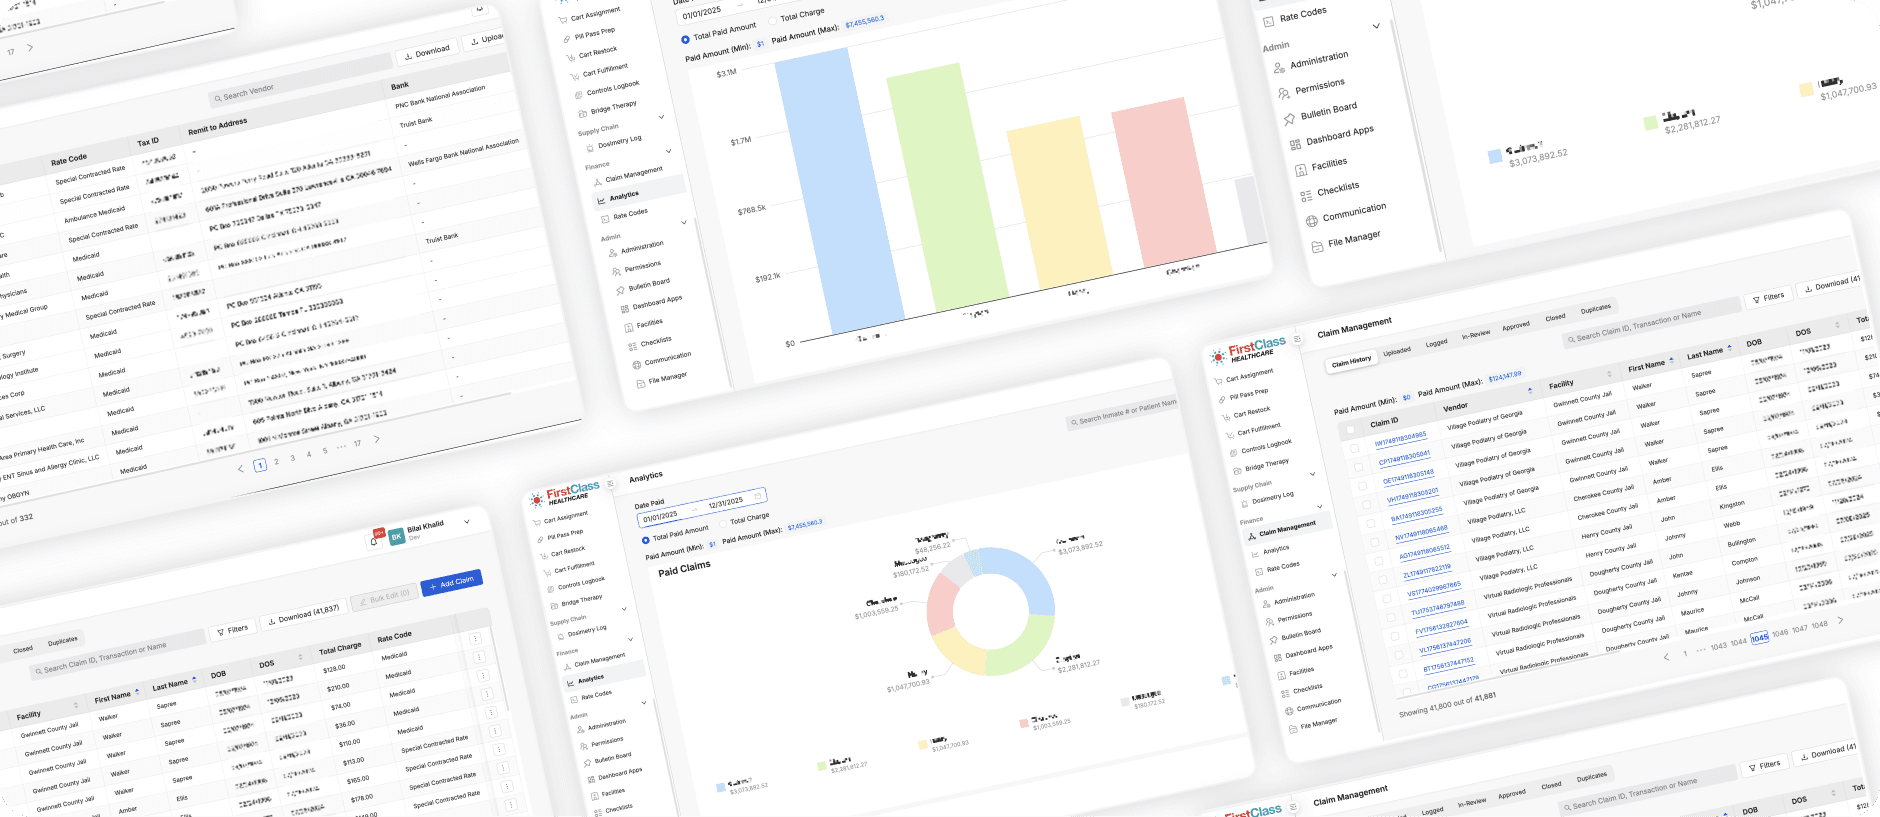
FirstClass Healthcare is a modern medical platform dedicated to streamlining patient care and data management. Because the platform handles electronic protected health information, its cloud foundation must satisfy HIPAA technical safeguards without slowing product delivery.
Carbonteq engineered a high-security infrastructure that automates access control, encryption, audit logging, vulnerability management, and private deployments across the platform.
Challenges faced by FirstClass Healthcare
HIPAA technical safeguards
The platform required robust encryption, unique user identification, automatic log-offs, and complete audit controls for electronic health information.
A private Kubernetes perimeter
The GKE cluster had to remain private while still supporting automated deployments from cloud-hosted CI/CD runners.
Zero-trust access
Medical staff, developers, and administrators needed tightly regulated, logged access without public management endpoints.
Continuous vulnerability management
Security flaws had to be detected and blocked before application code or container images could reach production.
HIPAA-aligned infrastructure and automation
Carbonteq combined private networking, automated security gates, layered edge protection, encryption, and centralized auditability into one production platform.
- •
Private access with Tailscale: A WireGuard-based private mesh gives authorized engineers secure access to private GCP clusters and databases without exposing public endpoints. Secrets are centrally vaulted and injected only at runtime, ensuring that ePHI-related credentials are never stored in code.
- •
Hardened CI/CD with Trivy: Trivy scans container images, file systems, and infrastructure-as-code. GitHub runner IPs are temporarily whitelisted only for the Helm deployment and revoked immediately afterward.
- •
Layered edge defense and encryption: Cloudflare and Google Cloud Armor provide DDoS and WAF protection. TLS 1.2+ protects data in transit and GCP-managed encryption protects data at rest.
- •
Monitoring, alerting, and immutable audit logs: GCP monitoring and uptime checks notify the SRE team via PagerDuty and Slack the moment a security threshold is crossed. Centralized immutable logs make infrastructure activity visible and compliance evidence available on demand.
Partnership and performance snapshot
- Category
- Compliance target
- Implementation detail
- HIPAA technical and administrative safeguards
- Category
- Network security
- Implementation detail
- Tailscale private mesh and Cloud Armor WAF
- Category
- Scanning
- Implementation detail
- Trivy integrated into CI/CD
- Category
- Deployment
- Implementation detail
- Private Kubernetes via Helm and dynamic whitelisting
- Category
- Monitoring
- Implementation detail
- GCP Cloud Logging and Monitoring
| Category | Implementation detail |
|---|---|
| Compliance target | HIPAA technical and administrative safeguards |
| Network security | Tailscale private mesh and Cloud Armor WAF |
| Scanning | Trivy integrated into CI/CD |
| Deployment | Private Kubernetes via Helm and dynamic whitelisting |
| Monitoring | GCP Cloud Logging and Monitoring |
Results
HIPAA-aligned infrastructure
Access control, audit controls, integrity safeguards, and transmission security are enforced through automated DevOps workflows.
Zero-exposure perimeter
Tailscale and private GKE remove public-facing management ports and sharply reduce exposure to brute-force attacks.
Automated compliance gates
CI/CD blocks every image carrying a critical vulnerability from reaching production.
Audit-Ready Transparency
With centralized logging and GCP Cloud Monitoring, the platform can generate detailed access reports in minutes, significantly reducing the overhead of compliance audits.
FirstClass Healthcare now has a foundation of trust that protects patient data without sacrificing the agility of a modern cloud-native platform.
Work with us
Ready to build something that lasts?
Every engagement starts with a real conversation. No proposals, no pitch decks. Just an honest look at what you’re building and whether we’re the right team to build it.